Business VLANs: how to segment your network step by step without breaking it
Business VLANs: which zones to create, addressing plan, flow matrix, trunks, firewall filtering and phased migration. Our method for SMBs in Morocco.
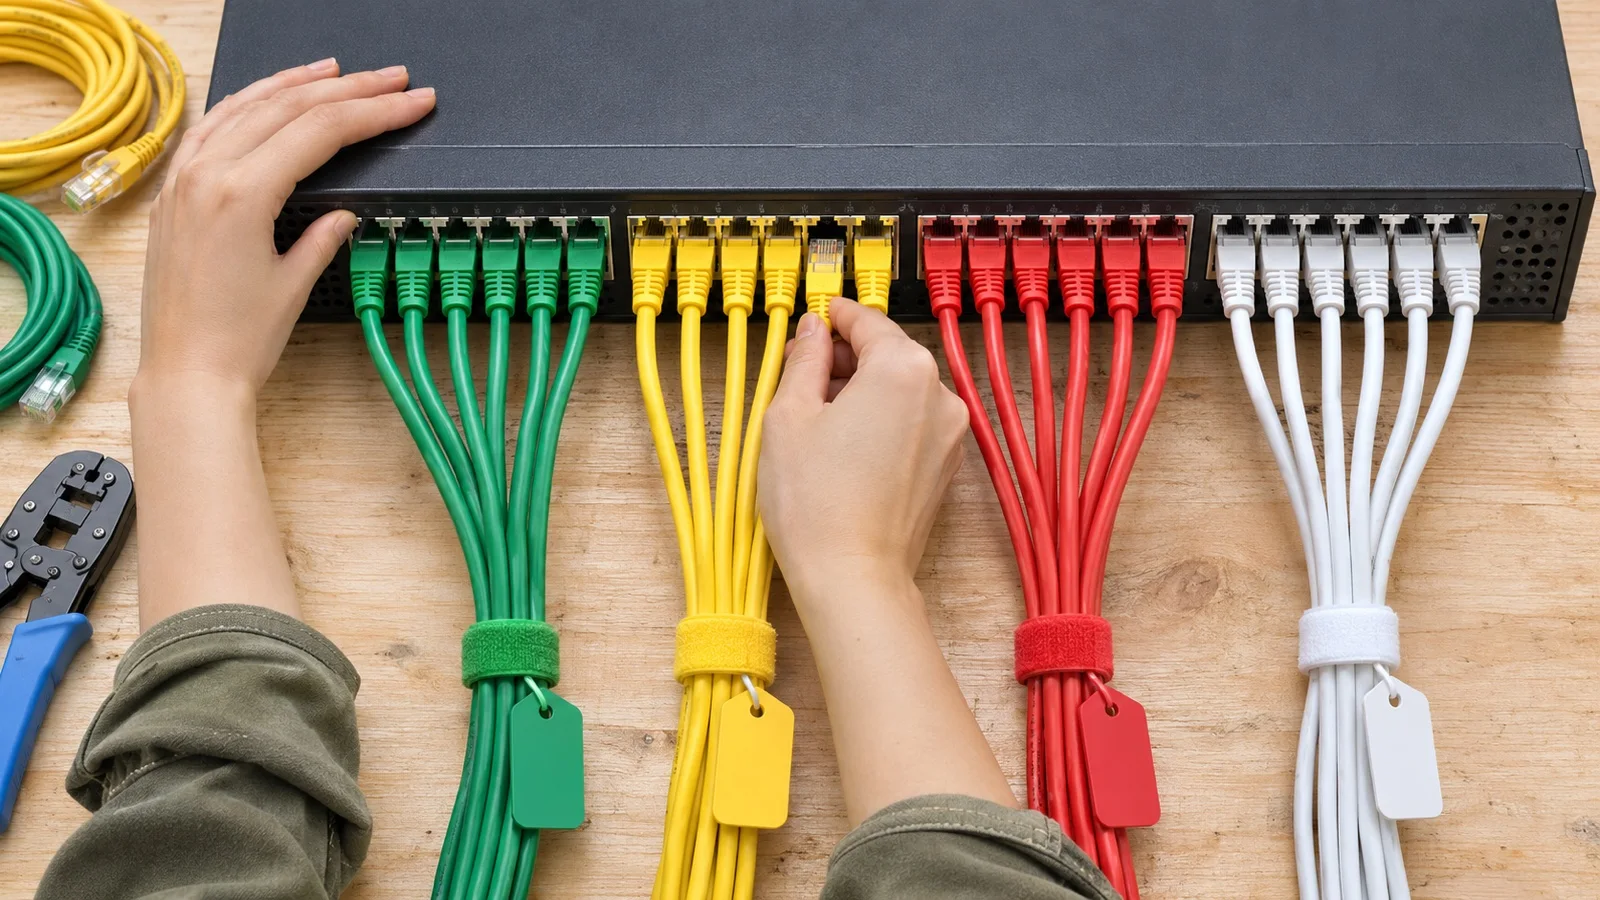
The short answer: a VLAN divides one physical network into several logical networks, but on its own it protects nothing. Security comes from filtering between those networks. To segment without breaking what already works, inventory your devices, create a small number of zones, write down who must talk to whom, then migrate one device family at a time and test at each step. The biggest risk is not technical: it is moving everyone at once without knowing which flows existed.
At ALLSAFE SOLUTIONS, in Casablanca, we carry out this kind of project as part of our network and WiFi infrastructure in Morocco work. This guide sets out the method we follow, based on the Cisco, Fortinet and WatchGuard documentation listed at the end. The VLAN numbers and addresses shown here are examples, to be adapted to your network.
Why segment: what a VLAN changes
On a flat network, workstations, servers, phones, cameras, printers and visitors all share the same space. A compromised camera or a workstation hit by ransomware can then try to reach everything else, without going through a single control. This is exactly what Zero Trust for SMBs aims to prevent, and it also matters against ransomware: it limits the spread.
Segmentation brings three concrete benefits:
- Security: an incident stays contained in its zone, and every exchange between zones goes through a rule.
- Quality: voice no longer suffers from other devices’ broadcast noise, a point covered in the mistakes that ruin call quality.
- Clarity: each zone has its own address range, which simplifies troubleshooting and monitoring.
Frameworks expect segmentation too: our PCI DSS guide for merchants explains why payment terminals benefit from isolation, and the US agency CISA recommends layering segmentation levels.
The concepts to master in five lines
| Concept | What it is | Key point |
|---|---|---|
| VLAN | Logical network identified by a number, standardised by 802.1Q | Usable IDs from 1 to 4094; some vendors reserve a few |
| Access port | Port tied to a single VLAN, untagged | For a workstation, printer or camera |
| Trunk port | Port carrying several tagged VLANs | Between switches, to the firewall, access points, a hypervisor |
| Native VLAN | VLAN whose traffic crosses a trunk untagged | Must match at both ends of the link |
| Inter-VLAN routing | Moving from one VLAN to another | Must go through a Layer 3 device: that is where you filter |
That last point is the heart of the matter. As Cisco points out, traffic between VLANs must be routed. If a Layer 3 switch handles that routing without access control lists, all your VLANs talk freely and the segmentation remains theoretical. For an SMB, we recommend sending this traffic through the firewall, which filters and logs it.
Step 1: inventory devices and flows
Before creating anything, list everything that is connected: workstations, servers, NAS, phone system, phones, access points, printers, cameras and recorder, time clocks, payment terminals, controllers. For each one, note the location, switch, port and IP address if it is fixed.
Above all, look for hidden dependencies: the time-tracking software that polls the clocks, the copier that drops scans on a server, the business application that calls a specific workstation, the recorder viewed from the manager’s office. These forgotten flows are what cause support calls the day after the cutover. Also check that your switches are managed: an unmanaged switch cannot separate VLANs, as we explain in patch rack and PoE switch: how to choose.
Step 2: define few zones, but the right ones
The right criterion is neither department nor floor, but level of trust and access needs. A zone only makes sense if it has its own rules.
| VLAN (example) | Zone | Subnet (example) | What goes in it |
|---|---|---|---|
| 10 | Workstations | 10.10.10.0/24 | Company computers, internal WiFi |
| 20 | Servers | 10.10.20.0/24 | Files, applications, domain controller |
| 30 | Voice | 10.10.30.0/24 | IP phones, phone system |
| 40 | Printing | 10.10.40.0/24 | Printers, copiers |
| 50 | Cameras and connected devices | 10.10.50.0/24 | Cameras, recorder, time clocks |
| 60 | Guests | 10.10.60.0/24 | Visitor WiFi, internet only |
| 90 | Management | 10.10.90.0/24 | Management interfaces of switches, access points and hypervisors |
| 999 | Unused ports | none | No address, no routing |
A simple tip: match the VLAN number to the third octet of the address. VLAN 30 and network 10.10.30.0 can be read at a glance during troubleshooting. Also check that these ranges do not overlap with another site linked by VPN, or with those found on remote workers’ home routers. If you keep backups on site, isolate them in a separate zone too, with very limited access.
Step 3: write the flow matrix
This is the most useful document in the project, and the one most often missing. It says who may initiate what towards whom, before anyone opens a console. Anything not listed is refused.
| From | To | Allowed | Example flow |
|---|---|---|---|
| Workstations | Servers | Yes, limited | File shares, business applications |
| Workstations | Voice | Limited | Softphone to the phone system |
| Workstations | Printing | Yes | Print ports only |
| Voice | Internet | Limited | Carrier SIP trunk, updates |
| Cameras | Internet | No | Remote viewing through VPN only |
| Guests | Internal network | Never | Internet only |
| Management | All | Yes | From a short list of workstations |
| All | Management | No | No access from other zones |
For IP cameras and multifunction printers alike, this logic avoids exposing devices that are rarely updated.
Step 4: create the VLANs, trunks and rules
Without placing any device yet, prepare:
- The firewall interfaces. On a FortiGate, each VLAN is a subinterface of a physical port linked to the switch over 802.1Q, with its own address, DHCP and rules. Traffic only passes between two VLANs once a rule exists, and replies to an established session come back automatically. On WatchGuard, each VLAN belongs to a zone (Trusted, Optional or External), and policies rely on those zones. We cover these products on our Fortinet integrator in Morocco and WatchGuard pages.
- The VLANs on the switches. With FortiSwitches managed through FortiLink, VLANs are created on the FortiGate, which pushes them to the switches; each port gets a native VLAN and a list of allowed VLANs, as explained in our FortiSwitch, FortiAP and Security Fabric guide.
- The trunks. On each link between devices, allow only the VLANs that are needed, not all of them.
- DHCP. One scope per VLAN. If the DHCP server is central, you need a relay, because broadcasts do not cross VLANs.
- The filtering rules, translated from the matrix, with logging.
Step 5: the cases that need particular attention
- Phone with a PC behind it. The switch port carries the workstation VLAN untagged and the voice VLAN tagged. The phone learns its VLAN through configuration, provisioning or LLDP-MED if the switch supports it. Traffic stays separate even on a single cable.
- WiFi access points. The access point’s port is a trunk, and each WiFi network (SSID) maps to a VLAN. Internal and guest WiFi share the same access point without sharing the same network, see our guide to deploying a business WiFi network.
- Automatic discovery. Discovery protocols for printers or wireless displays often rely on broadcasts that do not cross VLANs: plan a server print queue or a fixed address.
- Hypervisors. The host’s port is a trunk, and each virtual machine gets its VLAN on the virtual switch.
Step 6: migrate in batches and test both ways
Move one family at a time, in an order that limits risk: guests, then cameras and printers, then voice, then workstations, with servers last. For each batch, plan a simple rollback: the original configuration backed up, and the affected ports written down.
After each batch, test what must work (internet, applications, inbound and outbound calls, printing) but also what must fail: from guest WiFi, a server and a switch’s interface must remain unreachable. A positive test alone proves nothing about segmentation. Then watch the denials in the firewall logs: they reveal forgotten flows. Only add a rule if the need is justified and documented.
Harden the switches: six settings not to forget
- Do not use VLAN 1 for users or management. Cisco and WatchGuard advise against it: it is the well-known default VLAN, and it carries control traffic on Cisco switches, for example.
- Choose a dedicated native VLAN with no users, the same at both ends of the trunk.
- Put unused ports in a dead-end VLAN, with no DHCP, routing or management access, or disable them.
- Force port modes: no automatic trunk negotiation on user ports (DTP on Cisco).
- Isolate management: management interfaces in their own VLAN, reachable from a few workstations only.
- Enable access protections depending on the model: port security, DHCP snooping, NAC to place a device automatically in the right VLAN or in quarantine.
The mistakes we correct most often
| Mistake | Consequence | Fix |
|---|---|---|
| VLANs created, but a Layer 3 switch routes everything | No real separation | Send traffic through the firewall, or add access control lists |
| “Allow all” rule between zones | Segmentation exists only on the diagram | Start again from the flow matrix |
| All VLANs allowed on all trunks | One patching mistake exposes a whole zone | Limit each trunk to what is needed |
| Different native VLAN on each side | Traffic sent to the wrong VLAN | Align and document |
| Too many VLANs, without their own rules | Complex operations, no gain | Merge zones with the same needs |
| No documentation | Slow troubleshooting, rule drift | Keep the plan and matrix up to date |
The limits of VLANs
A VLAN replaces neither device updates, nor a properly configured firewall, nor strong authentication. Inside one zone, machines can still reach each other: two workstations on VLAN 10 can talk, unless specifically isolated (private VLANs, client isolation on guest WiFi, local filtering on workstations). You can go further by tightening segmentation around the most sensitive systems, but a simple segmentation that is really applied beats an ambitious architecture that nobody maintains. These settings belong as much to business cybersecurity in Morocco as to networking.
How we work
We start with a free initial audit: inventory, switch survey, identification of real flows and risks. We then deliver the VLAN and addressing plan and the flow matrix, for you to validate. We prepare the equipment, migrate in batches during windows agreed with your team, then test and document. We can supply the switches, access points and licences required, with or without installation. As part of our managed IT services in Morocco, the network is then monitored 24/7, and a critical incident is handled in under 15 minutes.
Request your free initial audit: we reply within 24 business hours and start by looking at what already exists, so as to reuse whatever can be reused.
Sources: Cisco, IOS XE VLAN configuration guide and VLAN best practices for Cisco Business routers; Fortinet, VLANs on FortiGate and VLANs on FortiSwitch through FortiLink; WatchGuard, about VLANs; CISA, layered segmentation.
Frequently asked questions
How many VLANs does an SMB need?
There is no official number. Start from the device families that do not share the same needs or level of trust: often workstations, servers, telephony, guests, cameras and connected devices, management. Only add a zone if it has its own filtering rules: a VLAN without specific rules adds complexity, not security.
Is a VLAN enough to secure a network?
No. It separates traffic at the switch level, but if a device routes freely between VLANs, an infected workstation can still reach the servers. Protection comes from filtering traffic between zones, usually on the firewall, and from switch settings. Inside a single VLAN, machines can still reach each other.
What is the difference between an access port and a trunk port?
An access port belongs to one VLAN and connects a workstation, printer or camera. A trunk port carries several VLANs using 802.1Q tagging and links switches to each other, to the firewall, to WiFi access points or to a hypervisor. A phone port with a PC behind it combines the untagged data VLAN and the tagged voice VLAN.
Do I need new switches to create VLANs?
You need managed switches that support 802.1Q. Unmanaged switches cannot separate VLANs: everything plugged into them stays on the same network. The inventory therefore tells you whether to replace all or part of your switches, or whether what you have is enough.
Can you segment without stopping the business?
Largely, yes, if you migrate in batches: create the VLANs and rules first without placing anyone in them, move one device family at a time starting with the least sensitive, test, then continue. Workstations and servers move last, in an agreed window, with a rollback ready.
About the editorial team
ALLSAFE SOLUTIONS
Network, security and cloud engineers
Written by the engineering team at ALLSAFE SOLUTIONS, a managed IT provider founded in Casablanca by network, security and cloud engineers. Our articles draw on the projects we deliver for clients in Morocco and abroad.
LinkedIn