FortiSwitch and FortiAP: managing the whole network from the FortiGate
FortiLink, built-in WiFi controller, NAC and Security Fabric: how the FortiGate manages your FortiSwitch switches and FortiAP access points from one console.
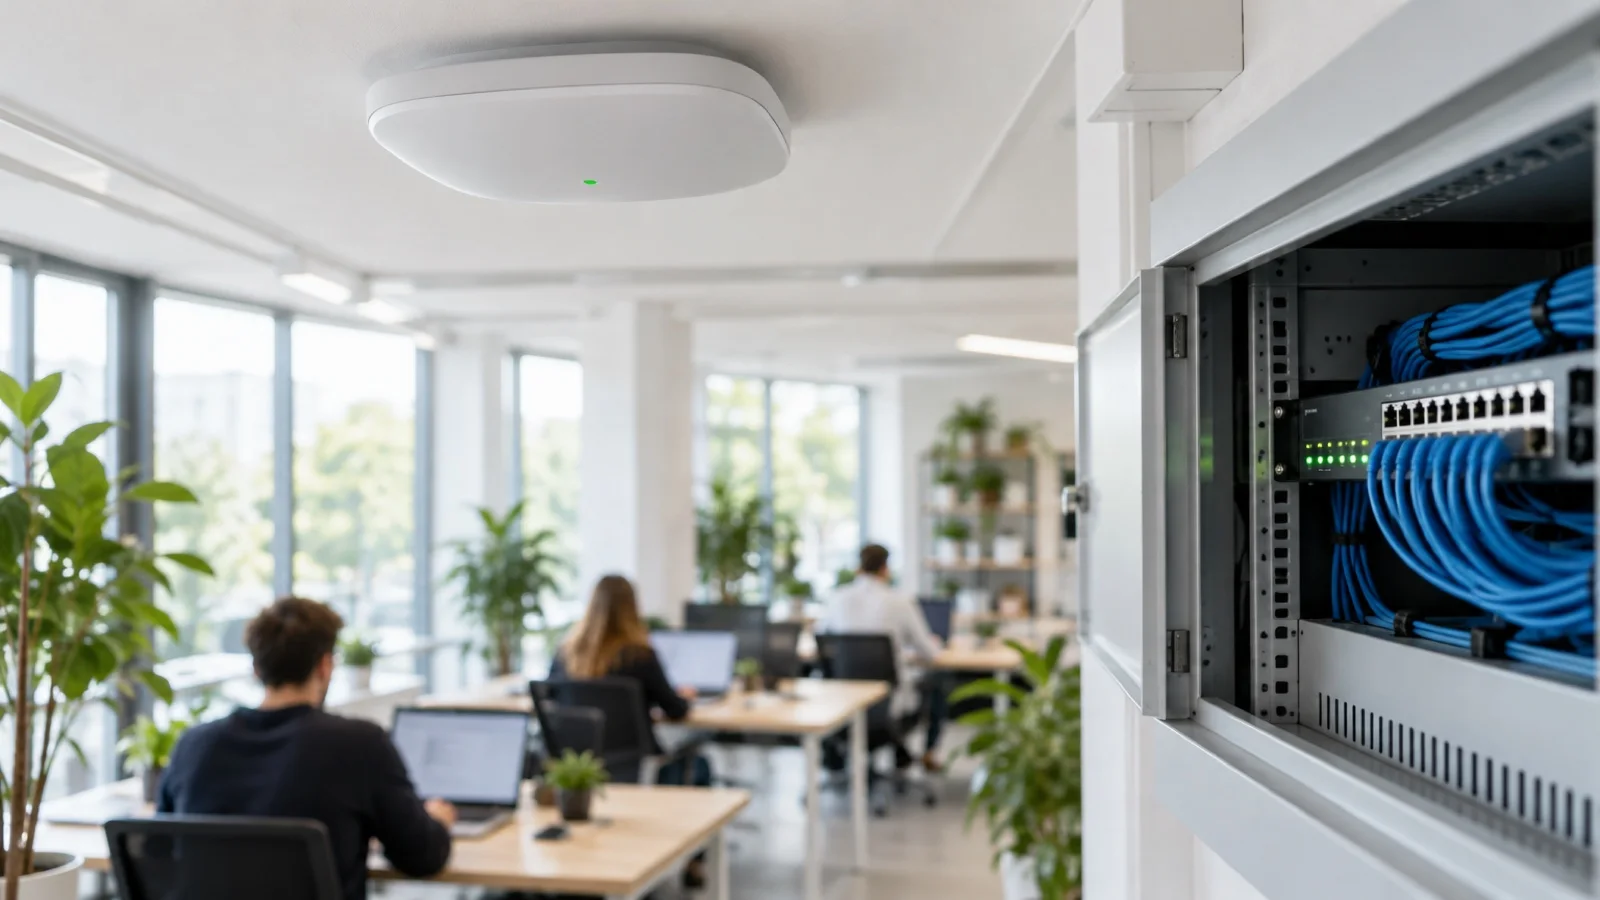
The short answer: if your firewall is a FortiGate, your FortiSwitch switches and FortiAP WiFi access points can be managed directly from it. The FortiLink protocol turns the FortiGate into the switch console; its built-in WiFi controller manages the access points, with no controller licence according to Fortinet; and NAC rules automatically place each device on the right network. The result: one place to configure, monitor and secure the whole network, which Fortinet calls the Security Fabric.
This article does not compare FortiAP with other WiFi brands, covered in Business WiFi: Ubiquiti UniFi or Fortinet FortiAP, nor does it revisit the choice of PoE switches, described in Patch rack and PoE switch: how to choose. It explains what an all-Fortinet architecture actually changes. At ALLSAFE SOLUTIONS, a Fortinet integrator in Morocco, we design and deploy these networks in Casablanca and across Morocco. Technical information comes from Fortinet’s official documentation.
The principle: the firewall becomes the network console
In a traditional network, each family of equipment has its own interface: the firewall on one side, the switches on another, the WiFi controller somewhere else. Creating a VLAN for cameras takes three separate operations, and mistakes creep in between consoles.
With FortiLink, Fortinet describes a different model: the FortiGate discovers connected FortiSwitches, authorises them, then manages their ports as if they were its own interfaces. FortiAP access points are managed the same way by the FortiOS WiFi controller. A VLAN is created once, on the FortiGate, and extended to switch ports and WiFi networks. The FortiGate also routes between these networks, with its security rules.
Day to day, this changes three things for the IT team or for the provider managing the network. Routine requests, such as connecting a new printer, adding an access point in a meeting room or isolating cameras, are handled from a single screen. Incidents are diagnosed faster, because you can see at a glance which device is plugged into which port and which access point it uses. And network documentation stays up to date on its own, since the reference configuration lives in the FortiGate and is backed up with it.
FortiLink: FortiSwitch managed from the FortiGate
FortiLink is the management protocol through which a FortiGate manages the FortiSwitch units connected to it. From the FortiGate interface, you set in particular:
- the VLANs assigned to each port: workstations, telephony, printers, cameras, guests;
- port PoE, to power IP phones, WiFi access points and cameras;
- link aggregation between switches and to the FortiGate;
- loop protection (spanning tree) and port security, including 802.1X authentication;
- switch firmware updates.
Two limits to know, documented by Fortinet. The number of FortiSwitches managed depends on the FortiGate model, and FortiLink is not supported when the FortiGate runs in transparent mode. We check both systematically at the sizing stage, using the grid in FortiGate for SMBs: which model to choose.
Physical design matters as much as configuration. Since every switch depends on the FortiGate for its management, we plan two FortiLink connections from the firewall, or from the cluster, to the first switch, and we place the switches so that losing one does not isolate an entire floor. Telephony, cameras and access points draw power from PoE ports: the power budget of each switch is checked against the real list of devices, with headroom for future additions.
FortiAP: the WiFi controller already in the FortiGate
Fortinet’s WiFi deployment guide is clear: all FortiGates include a full WiFi and switch controller in FortiOS, with no additional licence, either for the controller itself or for the number of access points managed. The only limit is the hardware capacity of the model.
Commissioning follows the order Fortinet describes: configure FortiLink, connect the FortiSwitch, create the VLAN for the access points, plug the FortiAPs into the switch, then authorise them from the FortiGate. Each WiFi network (SSID) then becomes a firewall interface, with its own rules: guest WiFi sees only the internet, internal WiFi reaches the servers, warehouse scanner WiFi talks only to the ERP. FortiGate security profiles (web filtering, antivirus, intrusion prevention) apply to wireless traffic just as to wired traffic.
For a very small site, there are also FortiWiFi units, FortiGates with built-in WiFi. As soon as you need to cover several rooms or floors, well-placed FortiAP access points give better results. For coverage design, see Enterprise WiFi for high density.
NAC: every device on the right network
Network access control (NAC) answers a simple question: what happens when someone plugs a device into a wall socket? Without NAC, it lands on the VLAN configured for that port, whatever the device. With FortiOS NAC, the FortiGate identifies the device and decides.
The FortiLink documentation describes several types of NAC policy:
| Policy type | What it recognises | Example use |
|---|---|---|
| Device | Vendor, family, type, operating system | IP phones go to the voice VLAN, printers to the print VLAN |
| User | Identity of the authenticated user | Accounting accounts access the finance VLAN |
| EMS tag | Device status reported by FortiClient EMS | A non-compliant workstation is isolated |
| Vulnerability | Severity level of vulnerabilities detected on the device | A vulnerable connected device is kept off the production network |
Fortinet provides ready-made VLAN templates, including a quarantine VLAN and an onboarding VLAN for devices not yet identified. Policies are evaluated in the order they are defined. In an SMB, this solves a very concrete problem: cameras, time clocks and printers ending up on the same network as management’s laptops. The logic matches Zero Trust for SMBs, and EMS tags are the same ones used for ZTNA, described in FortiClient VPN and ZTNA for remote work.
The Security Fabric: see and react in one place
The Security Fabric refers to the set of Fortinet products that share information around the FortiGate: switches, access points, devices running FortiClient, and other components as needed. For the IT team, this means:
- an overall view of the network: which device is plugged into which port, which access point serves which user;
- coordinated response: a suspicious device can be isolated on its switch port from the firewall;
- centralised logs, easier to use and retain;
- consistent updates, with compatible versions of FortiOS, FortiSwitch and FortiAP.
One point of caution: the FortiOS 7.6.3 release notes state that FortiGate models with 2 GB of memory no longer support the Security Fabric topology view or Security Rating. Before building a project on these features with an entry-level model, we check the unit’s memory and the target version.
Security Fabric value also depends on how it is run. Someone has to review the alerts, approve new devices waiting in the onboarding VLAN, and adjust NAC policies when the business adds a new type of equipment. Without that routine, quarantine VLANs fill up, users plug devices into unmanaged ports to get around them, and the architecture loses its point. We include these tasks in the monitoring we provide, with a regular review of new and unknown devices.
All Fortinet or mixed network?
| Situation | Our recommendation |
|---|---|
| New site or complete network refresh | FortiGate, FortiSwitch and FortiAP, managed together |
| Recent switches from another brand, still under warranty | Keep the switches, add FortiAPs, move to FortiSwitch at replacement time |
| Need for NAC or automatic isolation of connected devices | FortiSwitch needed to benefit fully |
| Very small office, single room | FortiWiFi, or a FortiGate and one FortiAP |
| Several branches | Same architecture model on each site, linked by SD-WAN with FortiGate |
| Firewall from another brand | No FortiLink: choose switches and access points suited to that firewall |
We stay pragmatic: replacing working switches purely for uniformity does not always make sense. An all-Fortinet architecture proves its value when it genuinely simplifies operations or brings security you actually need.
Mistakes we fix
- FortiSwitches bought and then managed one by one, without FortiLink: you pay for the integration without benefiting from it.
- A single FortiLink connection between the firewall and the first switch: if it is cut, the whole network is isolated.
- All devices in the same VLAN because segmentation “will come later”.
- FortiAP access points authorised automatically without checks, including unknown ones.
- Incompatible firmware versions across FortiOS, FortiSwitch and FortiAP after a partial update.
- A FortiGate model too small for the planned number of switches, access points and WiFi clients.
- Guest WiFi reaching the internal network, for lack of a dedicated rule on its interface.
Checklist before starting the project
- Inventory of devices to connect: workstations, phones, printers, cameras, connected devices.
- VLAN plan and traffic rules between them.
- Port count and PoE budget per switch, then number of access points and coverage plan.
- A FortiGate model able to manage the planned switches and access points, with enough memory for the intended features.
- Redundant FortiLink connections, and a firewall cluster if needed, see FortiGate high availability.
- NAC rules and quarantine VLAN.
- Support contracts for switches and access points.
How we work
We start with a free initial audit of your network: equipment in place, cabling, segmentation, WiFi coverage and FortiGate version. We then propose a suitable architecture, reusing what can be reused, and we supply FortiSwitch, FortiAP and licences, with or without installation. Deployment happens in stages, VLAN by VLAN, so business never stops. Once the network is in production, it is monitored 24/7, and critical incidents are handled in under 15 minutes.
Discover our network infrastructure and WiFi in Morocco offering and our partner statuses on the Certifications page, then request your free initial audit: we reply within 24 business hours.
Frequently asked questions
What is FortiLink?
FortiLink is the management protocol that lets a FortiGate manage the FortiSwitch units connected to it. The switches no longer have their own management interface to handle day to day: VLANs, PoE, link aggregation and port settings are configured from the FortiGate.
Is a licence needed to manage FortiAPs with a FortiGate?
Not for the controller: Fortinet states that all FortiGates include a full WiFi and switch controller in FortiOS, with no additional licence for the controller itself or for the number of FortiAPs managed. The limit is the hardware capacity of the FortiGate model. A support contract for the equipment should still be planned.
How many FortiSwitches can a FortiGate manage?
It depends on the FortiGate model: Fortinet publishes the maximum per model in its FortiLink documentation. We check it at the sizing stage, taking planned branches and extensions into account.
What does NAC do on a FortiSwitch network?
NAC (network access control) recognises the device plugged into a port, based on its type, its user, its FortiClient EMS tags or its vulnerability level, then automatically places it in the intended VLAN. An unknown device can be sent to an onboarding or quarantine VLAN.
Can we keep our current switches with a FortiGate?
Yes, a FortiGate works with any switch on the market. You simply lose centralised management, the overall view and NAC driven by the firewall. We often advise moving to FortiSwitch at the natural replacement cycle, not before.
About the editorial team
ALLSAFE SOLUTIONS
Network, security and cloud engineers
Written by the engineering team at ALLSAFE SOLUTIONS, a managed IT provider founded in Casablanca by network, security and cloud engineers. Our articles draw on the projects we deliver for clients in Morocco and abroad.
LinkedIn