Ransomware: 7 concrete measures to protect an SMB
Ransomware attacks target SMBs first. Here are the seven measures that stop the vast majority of attacks, in order of priority.
Every week, an SMB we audit discovers it would not have survived a ransomware attack. Not for lack of budget, but because the basics are not in place. For a business owner, the risk is concrete: invoicing stopped, customer files unreachable, production or front desk paralysed, and a ransom demand with no guarantee of getting anything back. Here are the seven measures we apply first, why they work, and how to put them in place without an enterprise budget.
How an attack unfolds
Ransomware almost never arrives in one go. An attack usually follows several stages, and each one is a chance to stop it:
- Entry: a password stolen through phishing, a poorly protected remote access, or an unpatched vulnerability.
- Foothold: the attacker tries to obtain administrator rights on a machine, then on the network.
- Spread: they move from machine to machine, locating servers and backups.
- Backup neutralisation: backups reachable from the network are deleted or encrypted first.
- Encryption and ransom: files become unreadable, often after data has been copied out, to add pressure with a threat of publication.
The seven measures below close these stages one by one. None is enough on its own, but together they stop the vast majority of attacks.
The 7 measures at a glance
| Measure | Stage blocked | Implementation effort |
|---|---|---|
| Off-site, immutable, tested backup | Backup neutralisation, encryption | Medium |
| MFA everywhere | Entry through a stolen password | Low to medium |
| Patching within 30 days | Entry through a known vulnerability | Medium, then recurring |
| Next-generation firewall | Entry, communication with the attacker | Medium |
| EDR on endpoints and servers | Foothold, spread, encryption | Low to medium |
| Least privilege | Foothold, spread | Medium |
| Training and a written plan | Entry through phishing, reaction time | Low, then recurring |
1. An offline, tested backup
The only guarantee against encrypted data is a copy the attacker cannot reach. It must be off site, immutable (impossible to alter for a fixed period) and restored in a test at least once a quarter. A backup that has never been restored is not a backup.
The 3-2-1 rule remains the reference: three copies of the data, on two different media, one of them off site. We add immutability, detailed in our guide to immutable 3-2-1 backup. An often-overlooked point: the backup console credentials must not be the company’s domain credentials. If the attacker takes over an administrator account, they must not be able to delete the backups with it.
2. Multi-factor authentication everywhere
A large share of intrusions start with a stolen password. Enable MFA on email, VPN, remote access and server administration. Administrator accounts come first.
The rollout needs preparing: account inventory, communication to staff, a fallback method for lost phones. We describe the approach in our MFA rollout guide. Prefer an authenticator app to SMS, and disable legacy email protocols that bypass MFA.
3. Patching within 30 days
The vulnerabilities exploited by ransomware often have a fix available for months. A monthly, automated and monitored patch cycle closes the most-used door.
The cycle must cover endpoint and server operating systems, but also what is often forgotten: browsers, business software, firmware on the firewall, switches and NAS, and any device exposed to the internet. Critical vulnerabilities on an exposed device are handled without waiting for the monthly cycle.
4. A firewall that actually inspects traffic
A carrier router is not a firewall. A next-generation appliance filters applications, blocks known malicious destinations and logs what goes in and out.
Inspection still has to be switched on and the rules kept up to date. A firewall configured at installation then forgotten, with “allow all” rules added over successive fixes, offers only a façade of protection. The logs also matter after an incident: they show where the attacker came in and which addresses they talked to.
5. Behavioural endpoint protection (EDR)
Classic antivirus recognises signatures. EDR detects behaviour: mass file encryption, privilege escalation, lateral movement. It isolates the machine before the attack spreads.
An EDR is only useful if someone watches its alerts and responds. Install it on servers too, not just on endpoints. The difference between the two approaches is explained in EDR vs antivirus for an SMB.
6. The principle of least privilege
No user should be a local administrator day to day. Service accounts get rights limited to their function. This drastically reduces the blast radius of a compromise.
In practice: a personal account for everyday work, a separate account reserved for administration, file shares open only to the departments that need them, and a regular review of accounts belonging to people who have left. Every unnecessary right is one more path for the attacker.
7. Trained users, and a written plan
A short quarterly phishing awareness session cuts click rates sharply. And a one-page recovery plan that says who calls whom, in which order, saves the hours that matter.
This plan sets two objectives: the RTO, the maximum acceptable downtime, and the RPO, the maximum amount of data you accept to lose, expressed as time since the last backup. They determine backup frequency and the order in which applications are restarted. The full method is in our disaster recovery plan guide.
What changes the effort
The work involved depends less on company size than on the starting point:
- The number of endpoints, servers and sites to cover.
- The state of the estate: obsolete systems that no longer receive patches, unsupported equipment.
- Remote work and remote access, to be secured one by one.
- Legacy business applications that require administrator rights to run.
- Whether a tested backup and network documentation already exist.
The most common mistakes
- A backup on a NAS on the same network, reachable with the domain administrator account.
- Remote desktop access open to the internet “for support”.
- MFA enabled for email, but not for the VPN or administrator accounts.
- An EDR installed, but nobody reading its alerts.
- A recovery plan that exists only in one person’s head.
If the attack is under way
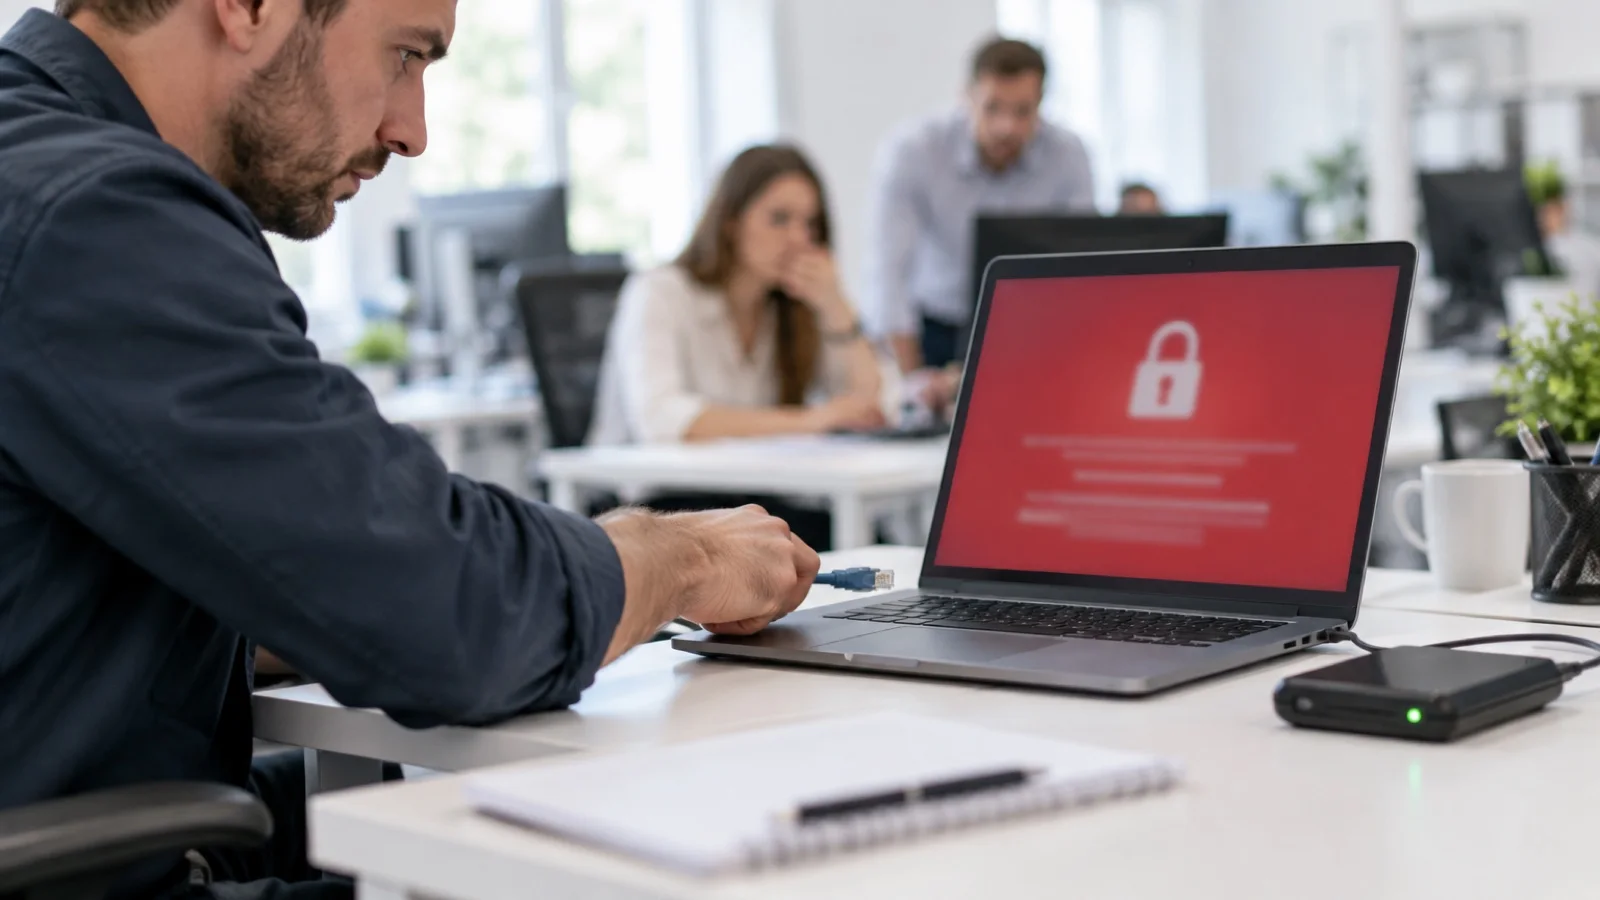
Isolate the affected machines and servers from the network, without shutting them down, to preserve traces useful for analysis. Cut remote access, alert your provider, then follow the written plan. Change passwords from a clean machine. Only restore once you understand how the attacker got in, otherwise they will come back the same way.
Checklist to verify this week
- Does an off-site, immutable copy of the data exist?
- When was the last restore test?
- Is MFA active on email, VPN and every administrator account?
- Are patches applied everywhere within 30 days, firewall included?
- Does an EDR cover endpoints and servers, and does someone follow its alerts?
- Who runs as administrator on their machine day to day?
- Does the recovery plan fit on one page, and does everyone know where to find it?
Taking action
These seven measures do not require an enterprise budget. They require method and follow-up. That is exactly what our business cybersecurity service covers, and the initial audit is free. To find out where your business stands on each of these measures, contact us.
Frequently asked questions
What is the first protection against ransomware?
A copy of your data the attacker cannot reach: off site, immutable for a fixed period, and restored in a test at least once a quarter. A backup that has never been restored is not a backup.
How does ransomware get into an SMB?
A large share of intrusions start with a stolen password, hence MFA on email, VPN and administration. Vulnerabilities with a fix available for months are the other most-used door.
Is the carrier’s router enough as a firewall?
No. Only a next-generation appliance filters applications, blocks known malicious destinations and logs what goes in and out.
What should you do first if ransomware is under way?
Isolate the affected machines and servers from the network without shutting them down, cut remote access, alert your provider, then follow the written recovery plan. Off-site, immutable backups are then used to restore.
About the editorial team
ALLSAFE SOLUTIONS
Network, security and cloud engineers
Written by the engineering team at ALLSAFE SOLUTIONS, a managed IT provider founded in Casablanca by network, security and cloud engineers. Our articles draw on the projects we deliver for clients in Morocco and abroad.
LinkedIn