FortiGate high availability: an active-passive HA cluster for SMBs
FortiGate high availability cluster: FGCP, active-passive or active-active, heartbeat links, licences on both units and upgrades without downtime.
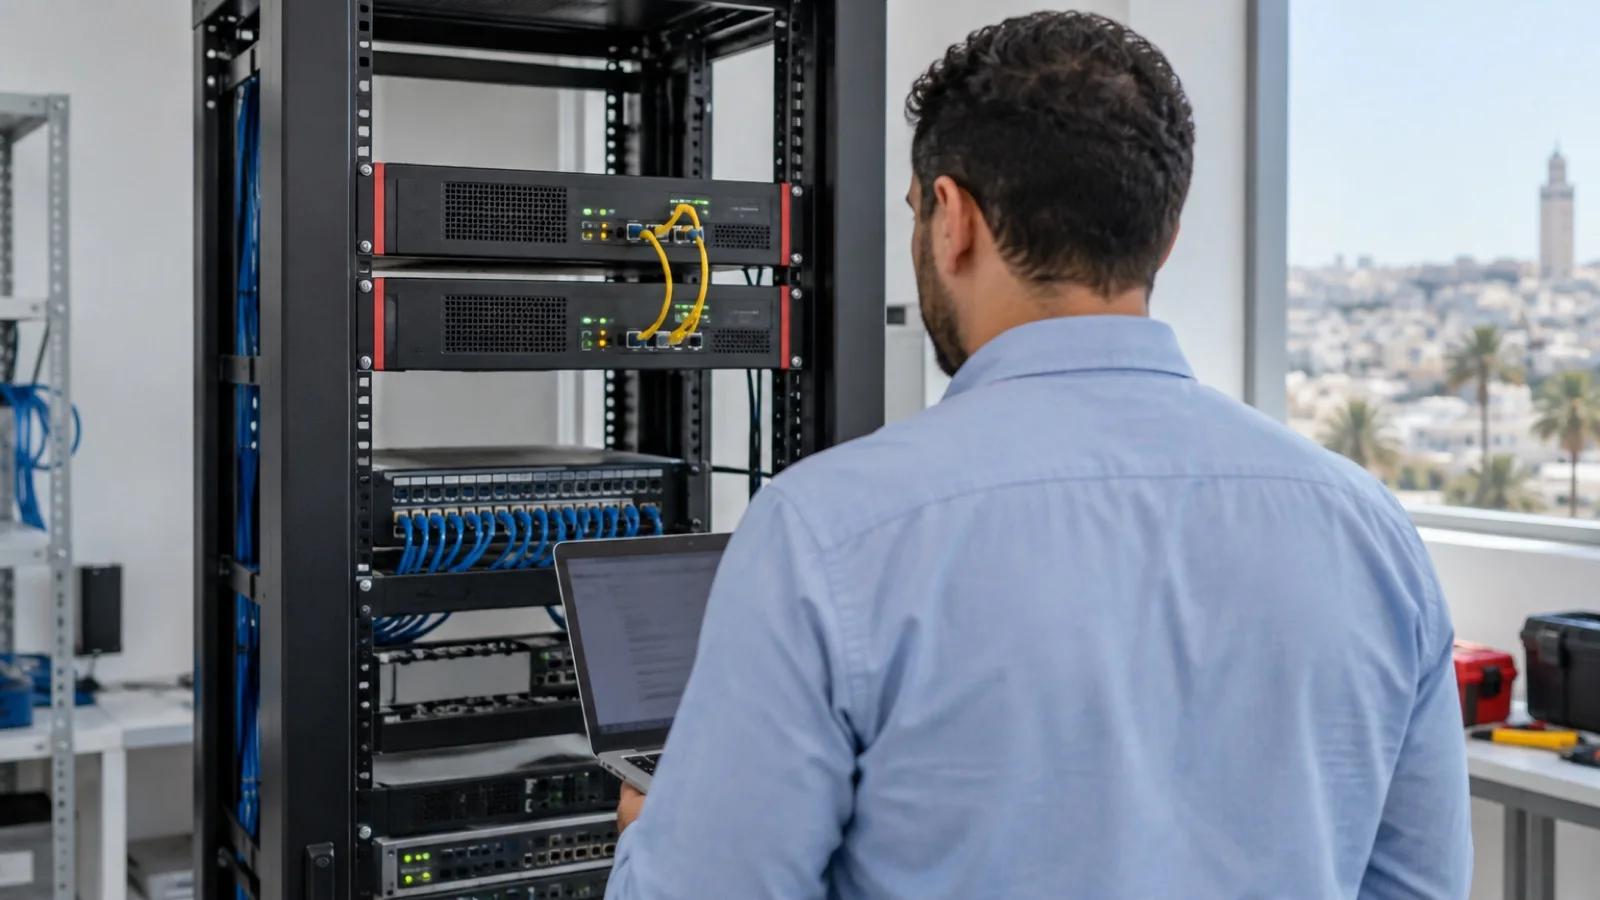
The short answer: a FortiGate high availability (HA) cluster pairs two identical units, same model and same FortiOS version, linked by two dedicated heartbeat cables. In active-passive mode, the first unit handles all traffic and the second takes over automatically if it fails or loses a monitored link. Configuration synchronises on its own between the two. On budget, each unit is normally licensed individually, except for Fortinet’s HA offer that shares one subscription on some entry-level and mid-range models. And a well-configured cluster upgrades without interrupting traffic.
This guide is for SMBs for which a firewall outage means production, tills or the phone system stop. It does not revisit model selection, covered in FortiGate for SMBs: which model to choose, but focuses on the two-unit architecture. At ALLSAFE SOLUTIONS, a Fortinet integrator in Morocco, we deploy these clusters in Casablanca and across Morocco. Technical details come from the FortiOS administration guide published by Fortinet.
Why a second FortiGate
In an SMB, the firewall is a single point of passage: internet, remote worker VPN, branch links, IP telephony, cloud applications. If it stops, everything stops. FortiCare hardware replacement solves the problem of the faulty unit, but not the hours of downtime between the failure and getting back into service with the right configuration.
An HA cluster addresses that specific risk. It does not protect against a fibre outage, against a configuration mistake, which will be synchronised to both units, or against ransomware. It is one building block of business continuity, to be placed in the broader approach described in Business continuity vs disaster recovery plan.
In practice, we recommend a cluster when several conditions come together: activity that cannot wait for a replacement unit (production, retail, healthcare, a contact centre), a phone system or business applications that depend on the firewall, branches or remote workers connected to head office, and an IT team or provider able to run it properly. Conversely, a small office whose activity can tolerate a short interruption is often better served by a second internet link, a configuration backup kept off the appliance and a responsive support contract. The decision is a business one before it is a technical one: what does an hour without the network cost you?
FGCP: Fortinet’s clustering protocol
FortiGate high availability relies on FGCP (FortiGate Clustering Protocol), a proprietary protocol through which units discover each other and form a cluster. According to Fortinet documentation:
- A cluster has at least two members, and the two-unit cluster is by far the most common.
- All members must be the same model, with the same firmware version and the same hardware configuration.
- HA settings must be identical on all units (mode, group ID, group name, password), except for each device’s priority.
- The primary unit synchronises the configuration to the others. Not synchronised: host name, HA priority, the override setting and dashboard widgets.
- Failover is triggered when the active unit loses power or a monitored interface loses its connection. For users nothing changes, except that the active device is different.
There is a second protocol, FGSP, which synchronises sessions between independent FortiGates. It suits more specific architectures; for an SMB, FGCP is the standard answer.
Active-passive or active-active
| Criterion | Active-passive (A-P) | Active-active (A-A) |
|---|---|---|
| Who processes traffic | The primary unit alone | The primary, which distributes part of the inspection to the second unit |
| What is distributed | Nothing | By default, proxy-based scanning: antivirus, web filtering, email filtering, data leak prevention |
| What stays on the primary | Everything | Sessions without security profiles, and HTTPS with deep inspection |
| HA offer licence sharing | Possible on eligible models | No: switching to A-A loses the virtual serial number |
| Ease of operation | High | Lower, trickier troubleshooting |
| Our use | Default choice for SMBs | Cases where proxy inspection saturates the unit |
Active-active looks more attractive, since both units work. In practice, its gain depends on the type of inspection: Fortinet states that HTTPS sessions with deep inspection are not load balanced, to avoid web filtering issues. Yet that is precisely the heaviest traffic in an SMB. If your FortiGate is saturated, the right answer is often a better-sized model, not an active-active cluster.
Heartbeat links and cabling
The two FortiGates talk constantly over the heartbeat links: health status, configuration synchronisation, and sessions if you enable it. The rules to follow:
- Two heartbeat links, cabled directly from one unit to the other, as Fortinet recommends. If there is a single link and it is cut, each unit may believe it is alone and become active: the scenario to avoid.
- The same ports on both sides: HA1 on one unit to HA1 on the other, and so on.
- Dedicated traffic: synchronisation uses TCP and UDP port 703 on these links.
- Each production interface cabled identically on both units, to a common switch. For a switch layer that does not itself become the single point of failure, see FortiSwitch and FortiAP managed from the FortiGate.
- Critical interfaces monitored (internet link, local network), so that losing a cable also triggers failover.
While the cluster forms, Fortinet warns that connectivity to the FortiGate may be briefly lost and that interface MAC addresses change. It is therefore done in a maintenance window, never in the middle of the working day.
Session synchronisation
By default, a failover drops current connections: users reload their page, remote workers restart their VPN. Session synchronisation (session pickup) lets the second unit resume existing sessions. Fortinet advises enabling it for day-to-day operation. It has limits depending on the type of traffic inspected; we test it during acceptance by deliberately triggering a failover during a phone call and a file transfer.
Licences on both units
This is the most commonly misunderstood point, and the one that weighs on the budget.
The general rule. The FortiOS administration guide states that most subscriptions and licences are not synchronised: each FortiGate in the cluster must be licensed individually. Two units means two FortiCare contracts and two FortiGuard subscriptions. A notable exception: FortiToken Mobile tokens are registered on the primary and synchronised to the second unit.
The shared HA offer. On the 40F, 60F, 70F, 80F and 100F series and their variants, Fortinet allows the two units of an active-passive cluster to share a single FortiGuard services subscription. The conditions are precise:
- order both units under the dedicated HA SKU;
- add a single Enterprise Protection, UTP or ATP bundle; à la carte services are not eligible;
- register the cluster on FortiCare, which links the two serial numbers into one virtual serial number;
- enable the “logical-sn” setting in the HA configuration, and never switch back to active-active, or you lose that virtual number and the associated services.
This offer is decided at purchase time, not afterwards. For renewal dates and bundle contents, see FortiGate licence renewal: FortiCare, UTP and deadlines. We supply appliances and licences, with or without installation, and check eligibility before ordering.
Upgrading a cluster without downtime
This is one of the least known benefits of a cluster. With uninterruptible upgrade, enabled by default, the FortiGate proceeds in this order, according to Fortinet documentation: upload the image, upgrade the secondary unit, fail traffic over to that upgraded unit, then upgrade the former primary. The “interrupted” mode, which upgrades all members at once, is faster but cuts traffic.
Two precautions remain essential. First, some upgrades do not support this mechanism: the target version’s release notes say so. Second, the official upgrade path applies to a cluster just as to a single unit. We detail the method in FortiOS upgrades: managing vulnerabilities safely.
Mistakes we fix
- A single heartbeat link, sometimes routed through a shared switch: at the slightest cut, two units active at the same time.
- A second unit of another model, or bought second-hand with another version: the cluster does not form.
- Licences bought for one unit only without the HA offer: after failover, the second unit runs without up-to-date security services.
- Switching to active-active “for performance” on a cluster that shared its licence, losing the virtual serial number.
- No monitored interface: the primary’s internet cable is unplugged, but the cluster does not fail over.
- A failover never tested since installation.
- A single switch behind both firewalls, which remains the single point of failure.
Checklist before ordering a cluster
- Identical model for both units, sized on throughput with inspection enabled.
- Eligibility for the shared HA offer, or budget for two subscriptions.
- Two free ports for heartbeat, and identical cabling on both sides.
- Upstream and downstream switches, ideally redundant.
- Interfaces to monitor and failover thresholds.
- Session synchronisation and test scenarios (call, VPN, transfer).
- Second internet link with SD-WAN, see SD-WAN with FortiGate.
- Upgrade procedure and maintenance window.
How we work
We start with a free initial audit of your network: FortiGate model and version, internet links, switches, critical applications. We tell you whether a cluster is justified, or whether a second link and a replacement contract are enough. If a cluster is justified, we supply the right appliances and licences, prepare the cabling, configure the cluster in a maintenance window and test failover in front of you. The cluster is then monitored 24/7: a failover triggers an alert, and critical incidents are handled in under 15 minutes.
Discover our network infrastructure and WiFi offering and our approach to managed IT services in Morocco, then request your free initial audit: we reply within 24 business hours.
Frequently asked questions
What is the difference between active-passive and active-active on FortiGate?
In active-passive, a single unit processes traffic and the other stands ready to take over. In active-active, the primary unit distributes part of the inspection work, notably proxy-based scanning, to the second unit. For an SMB, active-passive is simpler to run and troubleshoot; it is our default choice.
Do FortiGuard licences have to be bought twice for a cluster?
As a rule, yes: Fortinet states that each FortiGate in a cluster must be licensed individually. The exception: on the 40F, 60F, 70F, 80F and 100F series, a dedicated HA offer lets an active-passive cluster share a single services subscription, provided the units are ordered under the HA SKU with an Enterprise Protection, UTP or ATP bundle.
Can two different FortiGate models be combined in a cluster?
No. Fortinet documentation requires all cluster members to be the same model, with the same firmware version and the same hardware configuration, for example the same number of disks.
Does upgrading a FortiGate cluster cut internet access?
Normally not. With uninterruptible upgrade, the default setting, the FortiGate first upgrades the secondary unit, makes it take over the traffic, then upgrades the former primary. Some specific upgrades may be exceptions: always read the release notes first.
Does an HA cluster replace a second internet link?
No. The cluster protects against firewall failure. If your only fibre link goes down, both units lose internet. A second link from another carrier, managed with SD-WAN, covers that second risk.
About the editorial team
ALLSAFE SOLUTIONS
Network, security and cloud engineers
Written by the engineering team at ALLSAFE SOLUTIONS, a managed IT provider founded in Casablanca by network, security and cloud engineers. Our articles draw on the projects we deliver for clients in Morocco and abroad.
LinkedIn