Incident response plan: what to do in the first hour of a cyberattack
Incident response plan for SMBs in Morocco: first-hour actions (isolate without shutting down, preserve evidence, alert), roles and a one-page checklist.
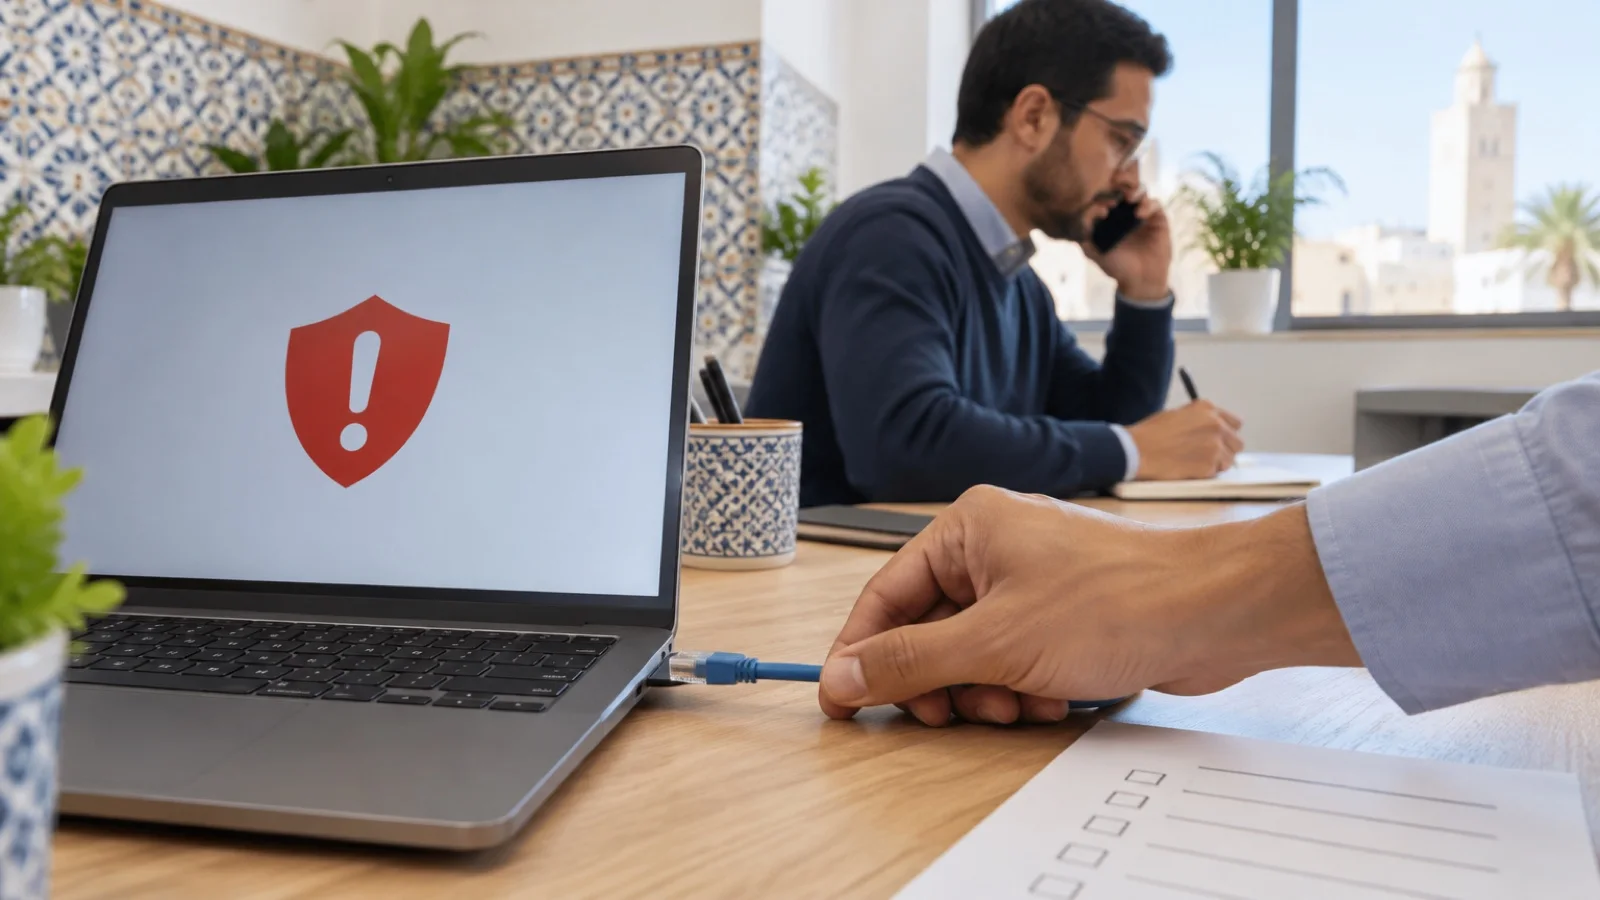
The short answer: in the first hour of a cyberattack, you are not trying to fix everything, you are trying to contain it. Five actions matter: isolate affected machines from the network without shutting them down, cut remote access and protect backups, alert the right people through a safe channel, write down everything that happens, and erase nothing before evidence has been preserved. These are simple actions, but under pressure they do not come naturally: that is why they must be written down beforehand, in an incident response plan.
At ALLSAFE SOLUTIONS, a managed IT provider in Casablanca, we write these plans with our clients and step in when an incident occurs, as part of our business cybersecurity in Morocco offering. This guide draws on NIST SP 800-61 Rev. 3 (April 2025), which ties incident response to the NIST CSF 2.0 framework, on the ransomware checklist from Cybermalveillance.gouv.fr and on the role of maCERT, the incident response centre of Morocco’s DGSSI.
Why the first hour decides what follows
Ransomware or an intrusion does not stop at the first workstation. The attacker goes after admin accounts, Active Directory, servers and backups. Every minute a compromised machine stays connected gives them time to move forward. Conversely, rushed actions make everything harder: shutting down every server erases evidence in memory, reinstalling a workstation before analysis destroys proof of the entry point, and paying “to go faster” guarantees nothing.
NIST makes the point in revision 3 of SP 800-61: incident response is not an isolated episode but part of risk management, prepared in advance (governance, asset identification, protection) and improved after each incident. A company that has prepared its first hour loses far less than one that improvises.
Signals that should trigger the plan
- files renamed with an unknown extension, or a ransom note on a workstation or server;
- antivirus or EDR alerts on several workstations at once;
- a mailbox sending emails its owner did not write, or unknown forwarding rules;
- an unusual payment request, or a supplier bank detail change received by email;
- sign-ins at unusual times or from unusual countries on the VPN or Microsoft 365;
- admin accounts created for no reason, backups deleted or failing.
At the slightest doubt, trigger the plan: a false alarm costs a little time, an ignored attack can cost weeks of business.
The first hour, step by step
| Step | Action | Who |
|---|---|---|
| 1. Right away | Disconnect the affected machine from the network (cable, Wi-Fi) without shutting it down; do not power on healthy machines that may be exposed | The user or first witness |
| 2. Immediately after | Call IT or the managed service provider; open the incident log | The witness, then the lead |
| 3. Contain | Isolate workstations through the EDR, cut VPN and remote desktop access, disconnect backups, block suspicious accounts | The technical team |
| 4. Measure the scope | Which machines, which accounts, which servers, is email affected | The technical team |
| 5. Decide | Inform management and decide next steps: partial shutdown, internal communication, call to the insurer, complaint, reporting | Management with the lead |
Isolate without shutting down
The first useful reflex is to disconnect: network cable pulled, Wi-Fi off. Cybermalveillance.gouv.fr recommends not shutting down affected machines, because doing so erases evidence held in memory; if encryption is still running, hibernation can be considered. If an EDR is deployed, its network isolation feature cuts the workstation off from everything except the security console, so it can be analysed remotely. We explain how this works in our EDR vs antivirus guide.
Cut access and protect backups
If the attack comes from outside, close the door: temporarily disable the VPN and remote desktop, or at least the suspicious accounts. Network-connected backups are a priority target for the attacker: disconnect them immediately. An offline or immutable backup, as described in our immutable 3-2-1 backup guide, is what lets you rebuild without paying.
If email is affected
For a compromised Microsoft 365 account: reset the password, revoke active sessions from the Microsoft Entra admin center, check and delete forwarding or deletion rules created by the attacker, review registered MFA methods, then warn contacts who may have received malicious emails. Preventive settings are covered in our 10 settings to secure Microsoft 365.
Alert through a safe channel
If the attacker is inside the IT system, they may be reading internal email. Crisis communication therefore goes through phone or a channel outside the affected system. That is why the contact list must exist on paper and in key people’s phones.
Write everything down
The incident log starts at minute one: time, what was observed, who did what. It is used for technical analysis, the insurer, the police complaint and the post-incident review. A simple sheet or a document outside the affected system is enough.
Mistakes to avoid
- Shutting down every server in a panic, which erases useful evidence and can complicate recovery.
- Reinstalling a workstation immediately, before understanding how the attacker got in.
- Plugging a backup drive into an infected machine “to check”.
- Discussing the incident over internal email, which the attacker may be reading.
- Paying the ransom: authorities advise against it, with no guarantee of recovery.
- Resuming business too early, without changing passwords or closing the entry point.
Who to alert in Morocco
| Contact | Why |
|---|---|
| IT department or managed service provider | Contain the attack, analyse, rebuild |
| Management | Decide on business shutdown, communication and spending |
| Insurer (if you have cyber cover) | Report the claim, access the assistance in the policy |
| Legal counsel | Assess obligations towards clients, partners and the CNDP if personal data is affected |
| Judicial police or public prosecutor | File a complaint, preferably before reinstalling machines |
| maCERT (DGSSI) | Incident reporting, mandatory for organisations covered by Law 05-20, and assistance |
| Bank | In case of payment fraud, request a block or recall of funds as fast as possible |
Reporting obligations under Law 05-20 are detailed in our guide to Law 05-20 and the DGSSI, and those related to personal data in our article on Law 09-08.
After the first hour
What follows tracks the classic incident response steps:
- Analysis: identify the entry point (malicious email, exposed remote access, unpatched flaw, stolen password) and everything the attacker did: accounts created, scheduled tasks, programs installed.
- Eradication: remove the attacker’s access, fix the flaw, change every affected password, starting with admin accounts.
- Rebuild: reinstall affected systems from clean installations, then restore data from a verified backup taken before the attack.
- Gradual restart under heightened monitoring, to catch any new attempt.
- Lessons learned: what worked, what was missing, and an updated plan.
The rebuild relies on your disaster recovery plan: without a tested backup, it can take weeks.
What a good incident response plan contains
- A one-page checklist, posted and known to everyone: disconnect, do not shut down, call this number.
- The contact list, internal and external, on paper and outside the IT system.
- Roles: who decides, who acts technically, who communicates, with a deputy for each.
- The inventory of critical systems and the order in which to restart them.
- The location of backups and a tested restore procedure.
- Emergency access: a protected break-glass admin account, firewall and console credentials kept in a safe place.
- An incident log template and message templates for staff and clients.
- A date for the next exercise.
How we do it
We start with a free initial audit: the state of backups, remote access, endpoint detection and email, and whether a procedure exists. We then write the checklist and the plan with you, and run a tabletop exercise. As part of our managed IT services in Morocco, our 24/7 monitoring team receives alerts from your workstations and firewalls, and a critical incident is handled in under 15 minutes, remotely, with on-site intervention from Casablanca when needed.
As a WatchGuard partner, Fortinet partner and Veeam partner, we deploy endpoint detection, network protection and backups that can withstand ransomware. Request your free initial audit: we reply within 24 business hours.
Frequently asked questions
Should a ransomware-infected computer be shut down?
In most cases, no. France's national victim-assistance service, Cybermalveillance.gouv.fr, recommends disconnecting the machine from the network (cable and Wi-Fi) without shutting it down, because shutting down erases useful evidence in memory. If encryption is still running, hibernation can be considered. Healthy machines that may be exposed should not be powered on either.
Who should be alerted first during a cyberattack?
First your IT department or managed service provider, who contains the attack. Then management, who decides, and depending on the case the insurer, legal counsel, the police to file a complaint and maCERT, the DGSSI's incident response centre. Organisations covered by Law 05-20 have a duty to report incidents.
Should the ransom be paid?
Authorities advise against it: there is no guarantee the data will be recovered, and payment funds further attacks. The real protection is an offline or immutable backup, tested regularly, which lets you rebuild without depending on the attacker.
What should an SMB incident response plan contain?
A one-page first-hour checklist, the list of internal and external contacts with numbers reachable outside the IT system, the roles (who decides, who acts technically, who communicates), the inventory of critical systems, the location of backups and the restore procedure, and an incident log template.
How often should the plan be tested?
At least once a year, through a one- or two-hour tabletop exercise built around a realistic scenario (ransomware, hacked mailbox, payment fraud), and after every major change: new provider, new critical application, departure of a key person. Each exercise reveals outdated contacts or missing steps.
About the editorial team
ALLSAFE SOLUTIONS
Network, security and cloud engineers
Written by the engineering team at ALLSAFE SOLUTIONS, a managed IT provider founded in Casablanca by network, security and cloud engineers. Our articles draw on the projects we deliver for clients in Morocco and abroad.
LinkedIn